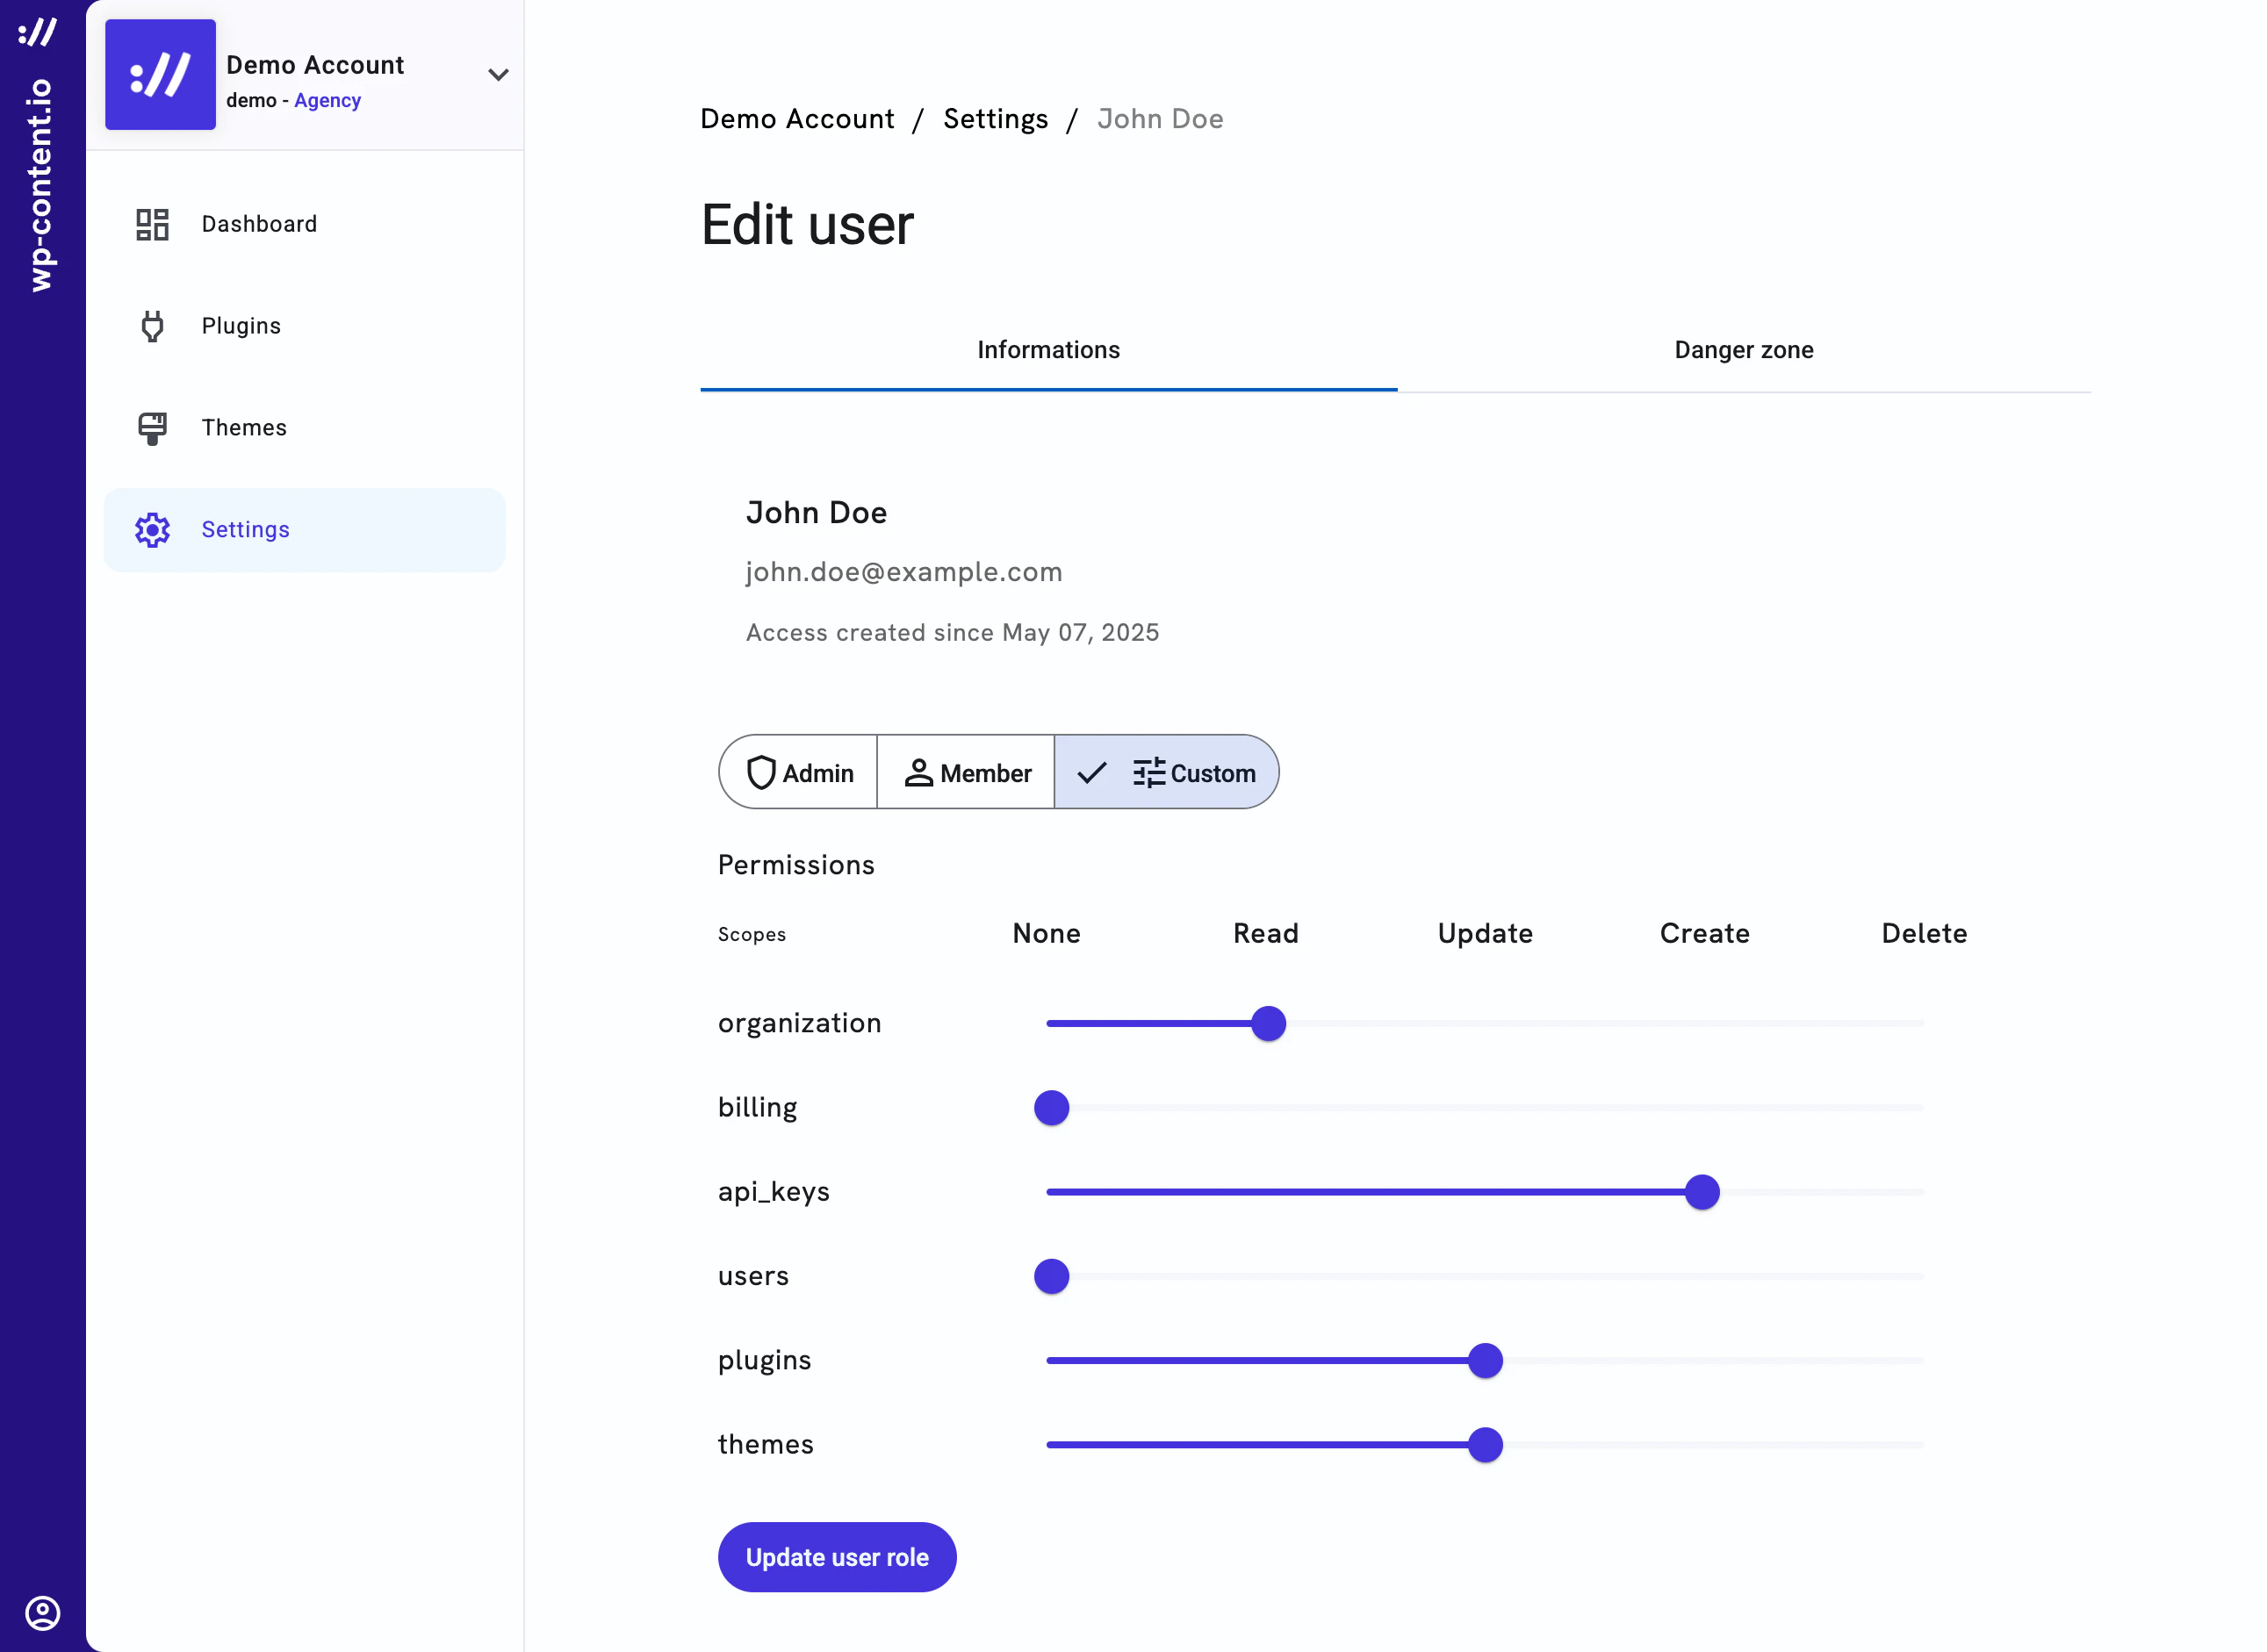
organization | View organization details | Update organization details | | |
billing | View billing information and invoice history | Update billing details or change subscription plan | Subscribe to a paid plan (if not already subscribed) | Cancel the active subscription |
api_keys | View API keys, their permissions and allowed domains | Edit an API key’s description and permissions, or enable/disable an allowed domain | Create a new API key with specific permissions | Revoke an API key or delete an allowed domain |
users | View organization members and their roles | Change a member’s role | Invite a new member to the organization or accept a pending invite | Remove a member from the organization |
plugins | View available plugins and their metadata | Upload a new ZIP version and edit plugin metadata (name, version, readme, etc.) | Add a new plugin to the registry | Delete a plugin from the registry |
themes | View available themes and their metadata | Upload a new ZIP version and edit theme metadata (name, version, readme, etc.) | Add a new theme to the registry | Delete a theme from the registry |